
Get the Best of Data Leadership
Stay Informed
Get Data Insights Delivered
An agent asks for a customer's address. The AI gateway authenticates the agent and confirms the tool call is approved. Every control passes. The address on file came from a dataset that missed its sync six hours ago, and nothing in the request shows it.
Access controls tell a team whether an agent may ask. Whether the answer it gets back is fit to use is a separate question, and most AI governance stacks leave it to a different team working on a different timeline.
That gap matters more as agents act on their own. In EY's September 2026 survey, 85% of organizations using agentic AI said those systems already act without real-time human oversight. When no one reviews an action before it happens, the authorization decision itself has to account for runtime context: who is asking, why, what they want to do, and the current state of the data the request touches. That gets harder as each agent connects to more tools and data sources, because every new connection brings data whose state can change from one request to the next. Agents need a guardian layer: a check on every action that sits outside any single agent, gateway, or environment and applies the same policy everywhere.
What we built
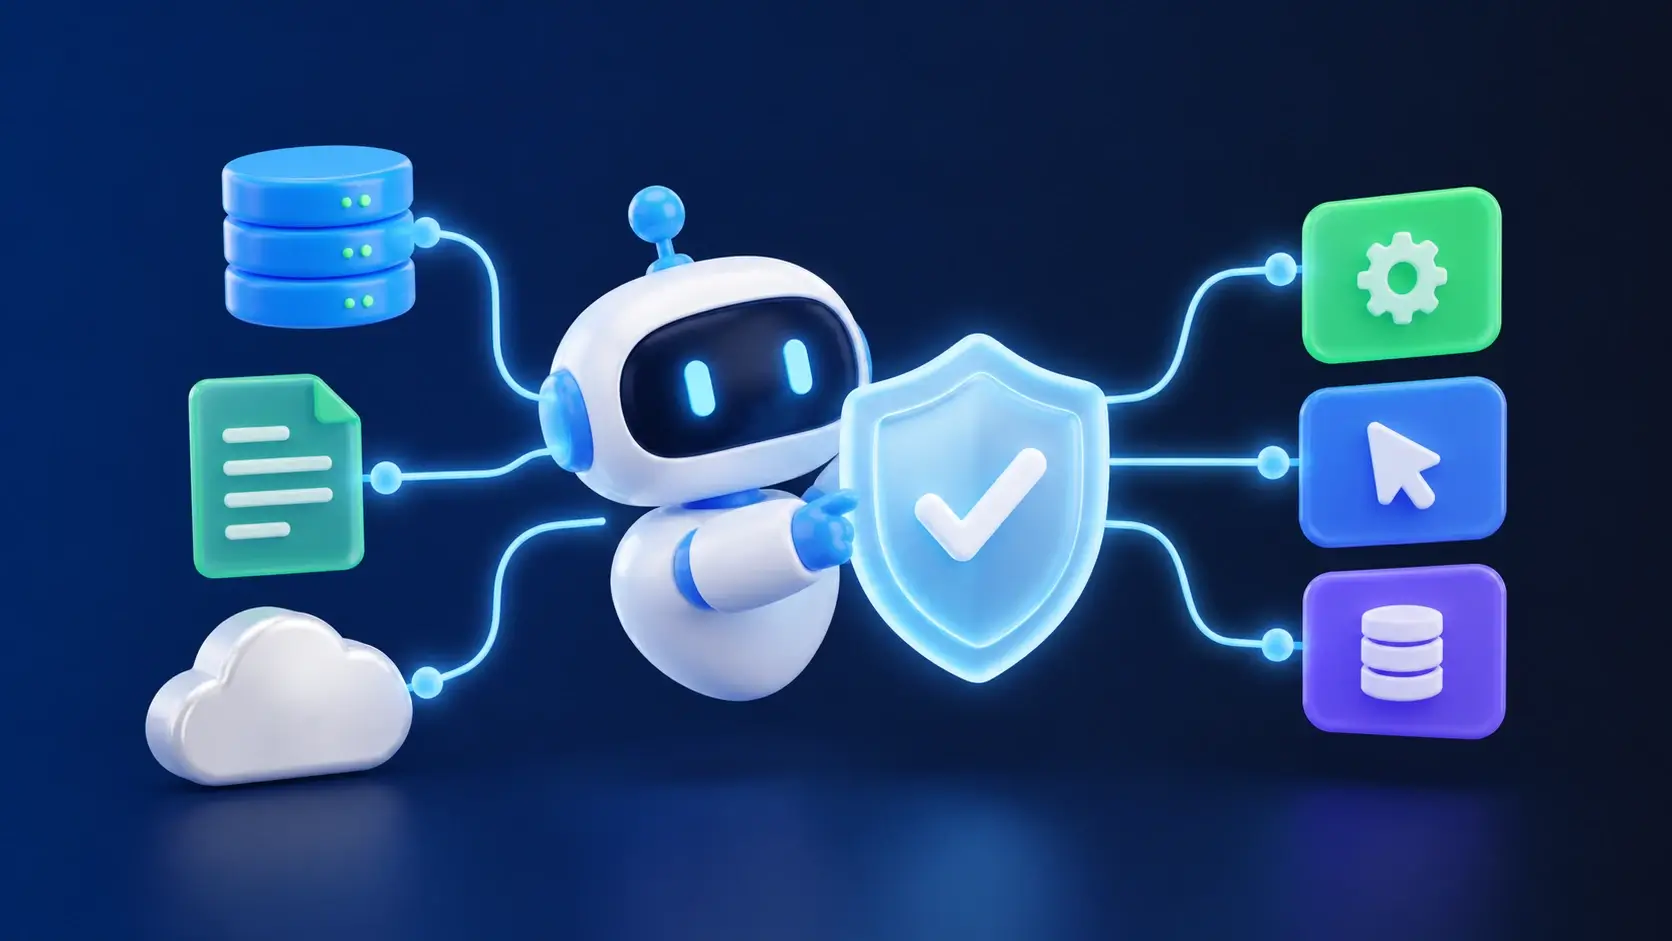
Most gateways can enforce a decision, but they need reliable, current data context to determine whether that decision is appropriate for the request. Policy Engine, now available in Agent Trust Hub, is that guardian layer. Traditional policies evaluate identity, permissions, and request attributes. Policy Engine adds the live state and lineage of the underlying data, allowing authorization to change when the data itself changes. It connects the quality, classification, lineage, and governance context Bigeye already maintains to the AI gateways enterprises run, starting with inaugural partners Kong, TrueFoundry, OpenLLM, Bifrost (by Maxim AI), Solo.io and Gravitee. A new integration framework lets other gateway providers connect to Policy Engine the same way. Here's the loop on every relevant request:
- The gateway authenticates the agent and resolves the request to a specific tool, dataset, or field
- Policy Engine checks who is asking, why, the requested action, and the current state of that data
- It returns a decision: allow, deny, restrict, or escalate to a person
- The gateway enforces the decision, and both the decision and the data state behind it go into one audit trail
If the dataset behind a request missed its refresh, the gateway can deny the request before the agent acts on outdated data. If a requested field is classified as sensitive, the gateway can redact it and return the rest.
Governance teams write policies against that data context, such as whether a dataset is certified, uncertified, stale, or classified as sensitive. The context also follows the data: if a raw customer identifier is restricted, lineage lets Policy Engine identify downstream datasets derived from it and carry that restriction forward.
Where to start
A practical way to start is to work in four steps:
- Discover. Agent Trust Hub automatically finds the agents running in production and the datasets they reach, so the starting point is what's actually running rather than what's documented
- Observe. See which datasets agents touch most and what state those datasets are in: certified, stale, sensitive, or not yet approved for AI use
- Act. Pick one written policy nobody can currently prove is enforced, such as access to customer financial data, and turn it into allow, deny, and require conditions for those datasets
- Attest. Review the first week of decisions with your Data, Security, and Compliance teams to confirm policies behave as intended and the audit trail shows enforcement, then extend coverage to more agents and datasets.
The goal isn't to remove human oversight everywhere. It's to make that oversight proportionate to risk. With a clear audit trail and measurable evidence of reliable behavior, teams can reduce checkpoints for lower-risk actions while maintaining tighter controls where the consequences are greater.
Agent autonomy should be earned, not assumed. That starts with policies that account for the state of the data and can show exactly why each action was allowed, denied, or escalated.
If your team is working through how to govern agent access, it's worth 15 minutes to watch Policy Engine evaluate a live request:
If your team builds or runs an AI gateway and wants to bring this data context into its own policy decisions, reach out to partners@bigeye.com to learn more about the integration framework.
Monitoring
Schema change detection
Lineage monitoring
Shane Wiggins
